 BreachModal
- Published
- Under
- Threat Intelligence
- Reference
- CVE-2026-85880
- Reading time
- 7 min
Actively Exploited Windows Zero-Days: Inside CVE-2026-85880
Summary
BreachModal's deep dive into the actively exploited Windows zero-days CVE-2026-85880 & CVE-2026-81963. Technical analysis, PoC, and mitigation.
Microsoft's September 2026 Patch Tuesday was not a routine update; it was an emergency response to two separate, actively exploited Windows zero-days that grant attackers full SYSTEM control over hundreds of millions of endpoints.
The flaws, tracked as CVE-2026-85880 (opens in a new tab) and CVE-2026-81963 (opens in a new tab), were confirmed by Microsoft as being used in active attacks before patches were available. According to Microsoft's own disclosure, CVE-2026-85880, a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), was reported by researchers at Volexity and Proofpoint. The second vulnerability, CVE-2026-81963, an improper link resolution flaw in the Windows Update Stack, was credited to Romain Deperne of Airbus Helicopters and the Microsoft Threat Intelligence Center (MSTIC). Both vulnerabilities carry a CVSS 3.1 score of 7.8, categorizing them as High-severity local privilege escalation (LPE) threats.
Note what this means: attackers are not just finding these flaws; they are weaponizing them before defenders even know they exist. The presence of two distinct LPE zero-days in a single patch cycle signals that the core Windows architecture remains a fertile ground for post-exploitation tooling, turning minor footholds from phishing or malware into total system compromise. This is not a failure of a single application, but a systemic weakness in the operating system's foundational components.
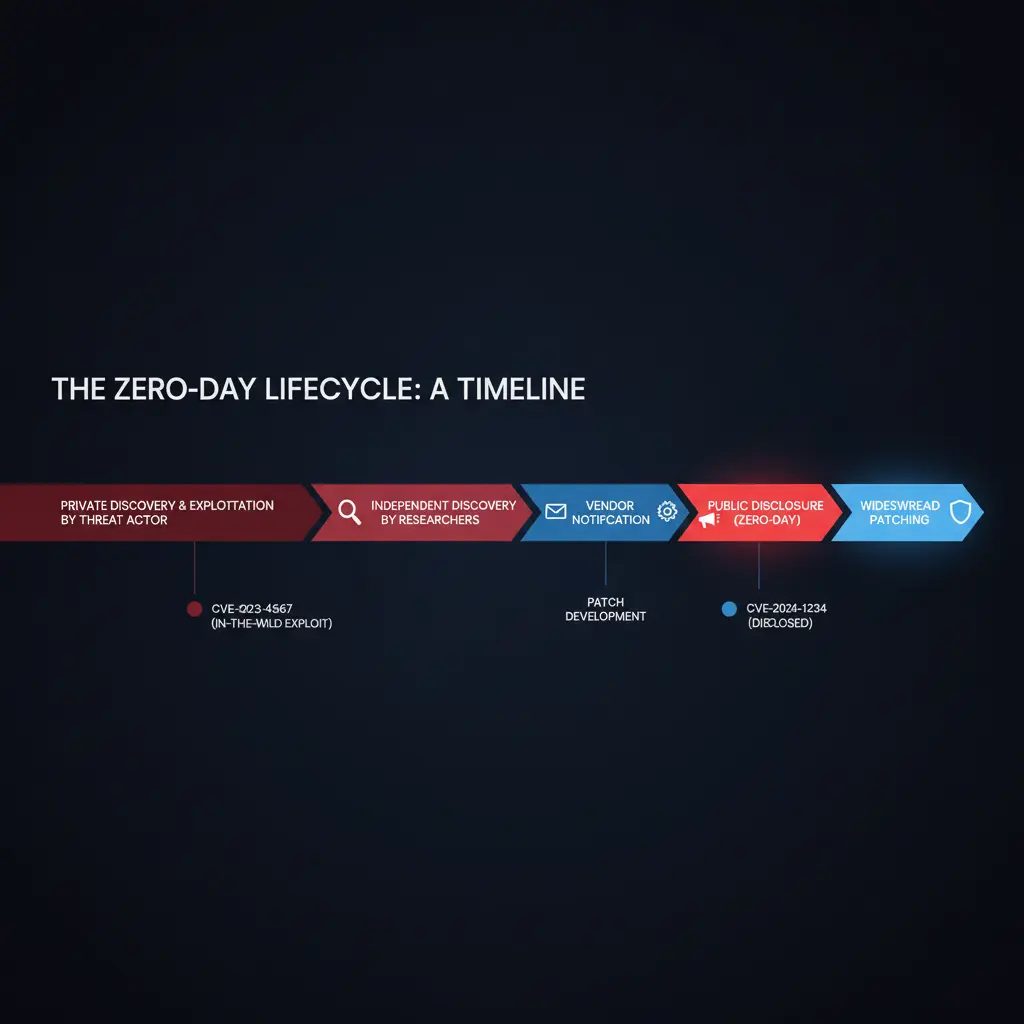
Anatomy of a Compromise: CVE-2026-85880
The first of the actively exploited Windows zero-days, CVE-2026-85880, is a classic memory safety vulnerability. It is a heap-based buffer overflow within the Advanced Local Procedure Call (ALPC) facility—a core inter-process communication system in Windows. An attacker who has already achieved code execution on a target, even with low privileges inside a restrictive AppContainer sandbox, can exploit this flaw to escape the sandbox and elevate their privileges to NT AUTHORITY\SYSTEM.
This is the attacker's golden key. Gaining SYSTEM privileges is equivalent to becoming the operating system itself, allowing the threat actor to disable security controls, deploy persistent rootkits, steal credentials from memory, and move laterally across the network. According to Microsoft's bulletin, the exploit requires no user interaction, making it a silent and effective second-stage payload. The flaw affects all currently supported versions of Windows 10 and Windows Server, a footprint that encompasses the vast majority of enterprise endpoints and servers globally.
The involvement of Volexity, a firm known for its incident response work against state-sponsored actors, suggests this vulnerability was likely discovered being used in targeted espionage campaigns. The implication is that sophisticated adversaries had this capability for an unknown period before its public disclosure.
The Update Stack Paradox: Dissecting CVE-2026-81963
The second zero-day, CVE-2026-81963, presents a particular irony. It is a link-following vulnerability in the Windows Update Stack, the very component responsible for delivering security patches. It is a particularly bitter pill to swallow when the mechanism designed to deliver security becomes a pathway for privilege escalation. This type of flaw, formally an "Improper Link Resolution Before File Access," allows an authorized but unprivileged attacker to manipulate the file system in a way that tricks a higher-privileged process into overwriting or creating arbitrary files.
An attacker with local access can create a symbolic link—a type of file system redirect—that points from a location where the Windows Update service expects to write a temporary file to a protected system location, such as C:\Windows\System32. When the update service runs with its SYSTEM privileges, it follows this malicious link and writes data to the protected file, potentially replacing a critical system DLL with a malicious payload. This is a textbook example of a Time-of-check to time-of-use (TOCTOU) attack.
This vulnerability's discovery by an aerospace security researcher alongside Microsoft's own threat intelligence team highlights the converged space of corporate and national security. The exploitation of such a fundamental OS component demonstrates a deep understanding of Windows internals, characteristic of well-resourced threat groups.
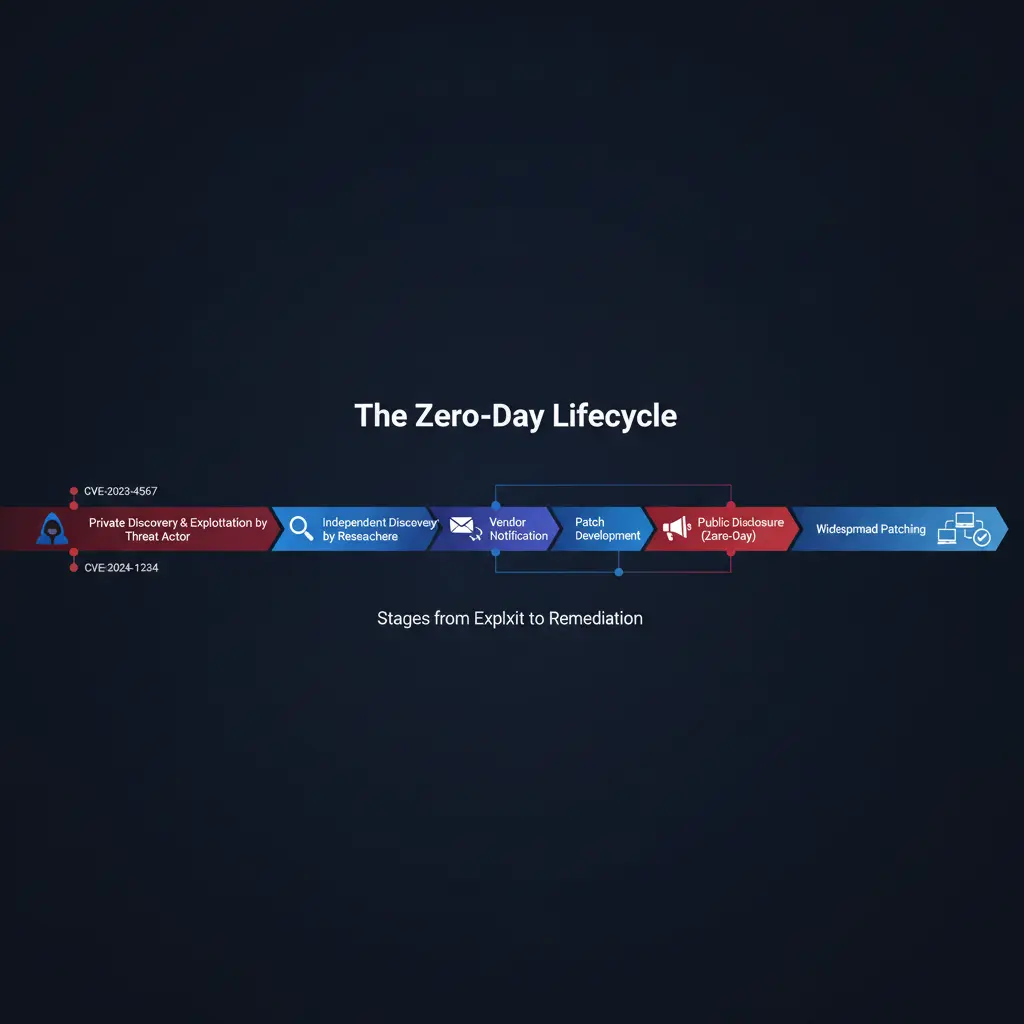
The Attacker's Calculus: Why LPE Zero-Days Are Gold
Neither of these actively exploited Windows zero-days provides initial access. An attacker cannot use them to break into a network from the outside. Instead, their value lies in the post-exploitation phase of an attack, as defined by the MITRE ATT&CK framework's T1068: Exploitation for Privilege Escalation (opens in a new tab).
Imagine an attacker gains a foothold through a successful phishing email, tricking a user into running a malicious macro. This initial payload runs with the user's standard privileges, which are limited. To achieve their objectives—data exfiltration, ransomware deployment, or espionage—the attacker needs administrative control. This is where CVE-2026-85880 or CVE-2026-81963 comes into play. The initial payload triggers the exploit, elevating its own privileges from 'User' to 'SYSTEM' in a single, swift action.
This escalation is critical for several reasons:
Persistence: With SYSTEM rights, an attacker can install services, create scheduled tasks, or modify the registry in protected locations to ensure their malware survives a reboot.
Defense Evasion: Administrative privileges allow malware to tamper with or disable endpoint detection and response (EDR) tools and antivirus software.
Credential Access: Tools like Mimikatz can be run to dump credentials, password hashes, and Kerberos tickets from memory, which requires the highest level of privilege.
Because these are zero-days, no signatures or behavioral rules existed to detect their specific exploitation patterns prior to September 8, 2026. Any organization without a rapid, emergency patching capability was vulnerable. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) recognized this immediate threat by adding both CVEs to its Known Exploited Vulnerabilities (KEV) catalog (opens in a new tab), mandating that federal agencies patch by September 22, 2026. This is not a recommendation; it is a directive based on active, ongoing threats.
Proof of Concept: Simulating a Link-Following LPE
This section provides a conceptual, high-level walkthrough for demonstrating the attack logic behind a link-following vulnerability like CVE-2026-81963. Note: This is a simulation and will not exploit the specific CVE but illustrates the technique.
Objective: Trick a privileged process (simulating the Windows Update service) into writing an attacker-controlled file into a protected directory (C:\Windows).
Prerequisites: Local access as a standard, unprivileged user on a Windows machine.
Step 1: Identify Target Directory & Create Payload First, the attacker identifies a directory where a privileged process is known to write temporary files. For this simulation, we'll use a predictable path. Then, create a simple payload file.
bash mkdir C:\Users\Public\UpdateTemp echo "[!] Malicious Payload" > C:\Users\Public\UpdateTemp\payload.dllThis step prepares the bait. The
payload.dllrepresents the malicious binary the attacker wants to place in a system directory.Step 2: Create Symbolic and Hard Links The core of the exploit is manipulating the file system. The attacker creates a directory junction (a type of symbolic link for directories) and a hard link to create a confusing path for the privileged process.
powershell **Requires the SeCreateSymbolicLinkPrivilege, often available to standard users** **or can be achieved via other means in a real attack.** cmd /c mklink /J C:\Users\Public\UpdateTemp\link_dir C:\WindowsThis command creates a junction point. Any process trying to access
C:\Users\Public\UpdateTemp\link_dirwill be transparently redirected toC:\Windows.Step 3: Trigger Privileged File Operation (Simulation) In a real exploit of CVE-2026-81963, the attacker would trigger the Windows Update client. In our simulation, we'll use a simple PowerShell command run as Administrator to mimic the privileged process writing a file.
powershell **Run this in an ADMINISTRATIVE PowerShell prompt** **This simulates the victim process.** Move-Item -Path "C:\Users\Public\UpdateTemp\payload.dll" -Destination "C:\Users\Public\UpdateTemp\link_dir\malicious.dll"The privileged
Move-Itemoperation intends to move the payload to a subdirectory, but becauselink_diris a junction toC:\Windows, it is tricked.Step 4: Verify Exploitation The attacker checks if the payload was successfully written to the protected system directory.
powershell **Run as the standard user** Test-Path C:\Windows\malicious.dllIf this command returns
True, the exploit was successful. The unprivileged user has successfully written a file intoC:\Windows, bypassing standard security permissions. In a real attack, this file would be a malicious DLL targeted for a DLL hijacking attack, leading to code execution as SYSTEM.
FINAL VERDICT
The September 2026 actively exploited Windows zero-days place the burden of risk squarely on organizations with slow patch management cycles. CVE-2026-85880 and CVE-2026-81963 are not theoretical vulnerabilities; they are confirmed weapons in the hands of active adversaries, transforming low-level intrusions into full-blown, administrative-level compromises. The pattern is clear: assume initial access will occur. The critical control is preventing that access from becoming administrative control. Organizations that treat Patch Tuesday as a routine, non-urgent process are choosing to accept the risk of complete system takeover. The only effective mitigation is immediate, prioritized patching of these specific vulnerabilities.
Your security posture is only as strong as your response time to active threats. BreachModal's Adversarial Simulation services can validate your defenses against multi-stage attacks that leverage privilege escalation techniques just like these. Contact us to test your resilience. (opens in a new tab)