
SOC 2 Type II in 90 Days: A Realistic Preparation Guide
A practical, non-consultant-speak breakdown of how to achieve SOC 2 Type II readiness without burning your engineering team.
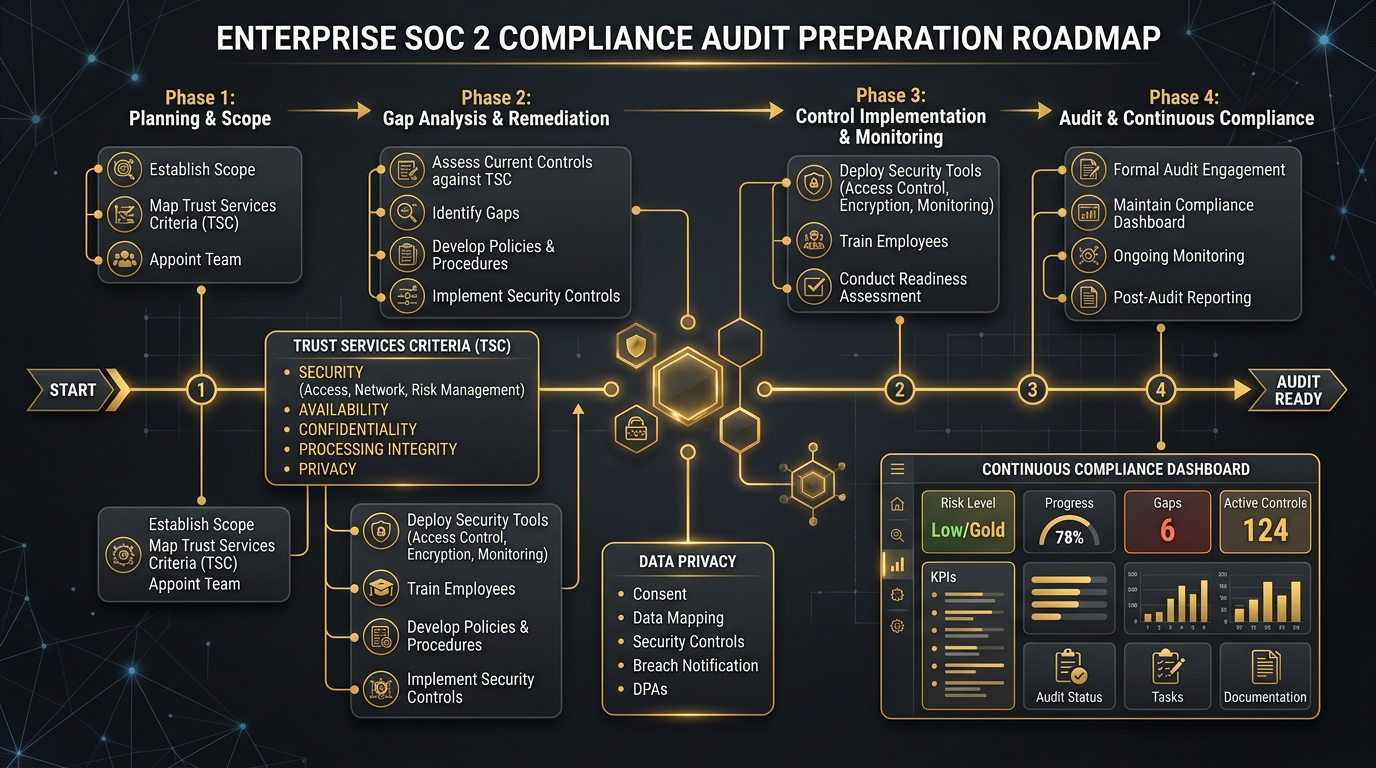
SOC 2 has a reputation for being painful and expensive. Most of that pain is avoidable with the right sequencing.
What Actually Gets Tested
SOC 2 Type II tests five Trust Service Criteria: Security (mandatory), Availability, Confidentiality, Processing Integrity, and Privacy. Unless your customers contractually require all five, start with Security-only. You can expand scope in Type III.
The 90-Day Timeline
Days 1–30 are gap assessment. Map your existing controls to the CC criteria. Most engineering teams are surprised to find they already have 60–70% of required controls in place — they just aren't documented.
Days 31–60 are remediation sprint. Close the gaps you identified. Common gaps: access review cadence, formal change management, vendor risk assessments, and incident response runbooks. These sound scary but are mostly documentation work.
Days 61–90 are evidence collection and auditor readiness. Your auditor will test controls over a period (usually 6–12 months for Type II). Start that observation window as early as possible.
Tools That Actually Help
Vanta, Drata, and Secureframe automate evidence collection and map it to criteria. But they don't replace judgment — someone on your team needs to understand what each control is testing.
The BreachModal Shortcut
Our compliance intelligence layer monitors your cloud estate continuously and maps evidence to SOC 2, ISO 27001, HIPAA and GDPR in real time. When audit season arrives, your evidence vault is already full.
Want this expertise working for your team?
Schedule a 30-minute call and we'll walk through your specific security posture.
Book a consultation