
The 27-Minute Zero-Day Response Playbook
How elite security teams contain novel exploits before they cascade — a step-by-step framework used across 600+ production databases.
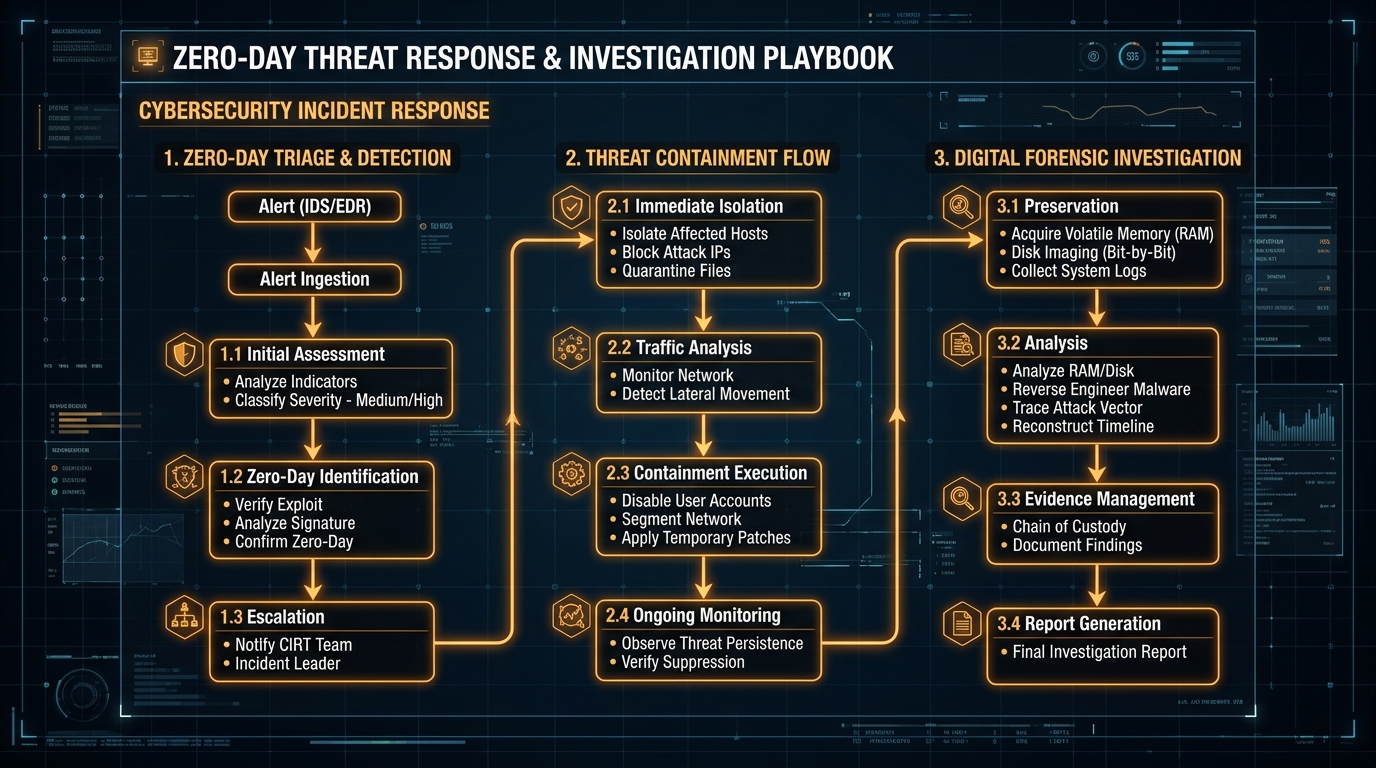
When a zero-day lands in production, the clock starts immediately. Most teams waste the first 15 minutes in Slack threads and escalation chains. Here's the framework that cuts that to zero.
The First 5 Minutes: Triage Without Drama
The moment an alert fires, your automated playbook should already be isolating affected systems. Manual triage is the enemy of containment. BreachModal's AI incident command module classifies severity, identifies blast radius, and drafts your stakeholder brief before a human has opened their laptop.
Minutes 5–15: Containment
Network segmentation is non-negotiable. If your cloud architecture doesn't allow instant segment isolation via API call, that's your most expensive technical debt. Pair this with credential rotation for any service accounts that touched affected systems.
Minutes 15–27: Evidence Preservation
Forensic integrity matters for regulatory reporting and litigation. Snapshot affected instances, preserve logs in immutable storage, and begin your chain-of-custody documentation. GDPR and HIPAA both have notification windows that start counting from the moment you *should have known* — not when you eventually discovered it.
Post-Incident: The Narrative That Protects You
Board members and regulators don't read log files. They read narratives. Your incident report should tell a story: what happened, what you did, what you're doing to prevent recurrence. That story is your legal and reputational shield.
Want this expertise working for your team?
Schedule a 30-minute call and we'll walk through your specific security posture.
Book a consultation