 BreachModal
- Published
- Under
- Threat Intelligence
- Reading time
- 5 min
VOLTZITE Grid Espionage: SCADA Zero-Days & Pre-Positioning
Summary
Analysis of PRC actor VOLTZITE targeting US and NATO power grids via SCADA zero-days, edge appliances, and living-off-the-land operational tradecraft.
China's advanced persistent threat operators are no longer staging for corporate espionage; they are pre-positioning logic bombs inside Western electric utilities. The operational technology cluster tracked by Dragos as VOLTZITE—congruent with Microsoft's Volt Typhoon, CrowdStrike's Vanguard Panda, and Secureworks' BRONZE SILHOUETTE—has systematically penetrated North American and allied European transmission operators by executing targeted zero-day exploits against internet-facing network appliances. Drawing support from access broker group SYLVANITE, the campaign compromises edge routers, SD-WAN controllers, and remote monitoring systems to access engineering boundaries before quietly harvesting the exact physical blueprints necessary to disrupt civil society.
Evidence declassified by the Federal Bureau of Investigation (FBI), the National Security Agency (NSA), and the Cybersecurity and Infrastructure Security Agency (CISA) paints a stark trail of intrusion. In the breach of Littleton Electric Light and Water Departments (LELWD), VOLTZITE operators maintained an unhindered dwell time of over 300 days across dual-homed management assets. Leveraging edge flaws cataloged in the CISA Known Exploited Vulnerabilities Catalog (opens in a new tab)—including the Versa Director flaw CVE-2024-39717 (opens in a new tab) and Ivanti gateways (CVE-2023-46805 (opens in a new tab) and CVE-2024-21887 (opens in a new tab))—the threat group successfully introduced the memory-resident VersaMem web shell into upstream management tiers. In an ironic twist of enterprise hygiene, operators often used the utility's own administrative automation tools to shut down alarms that would have revealed their presence, proving once again that the most dangerous software in your network is the software you paid for.
Note what this means: This is not intellectual property theft or financial extortion. When an adversarial military intelligence entity maps out Remote Terminal Units (RTUs), Geographic Information System (GIS) layouts, and single-line operational schematics, their return on investment is counted in sub-station kinetic blackouts, not ransoms.
The Silent Train: Obfuscation and Dynamic Proxy Routing
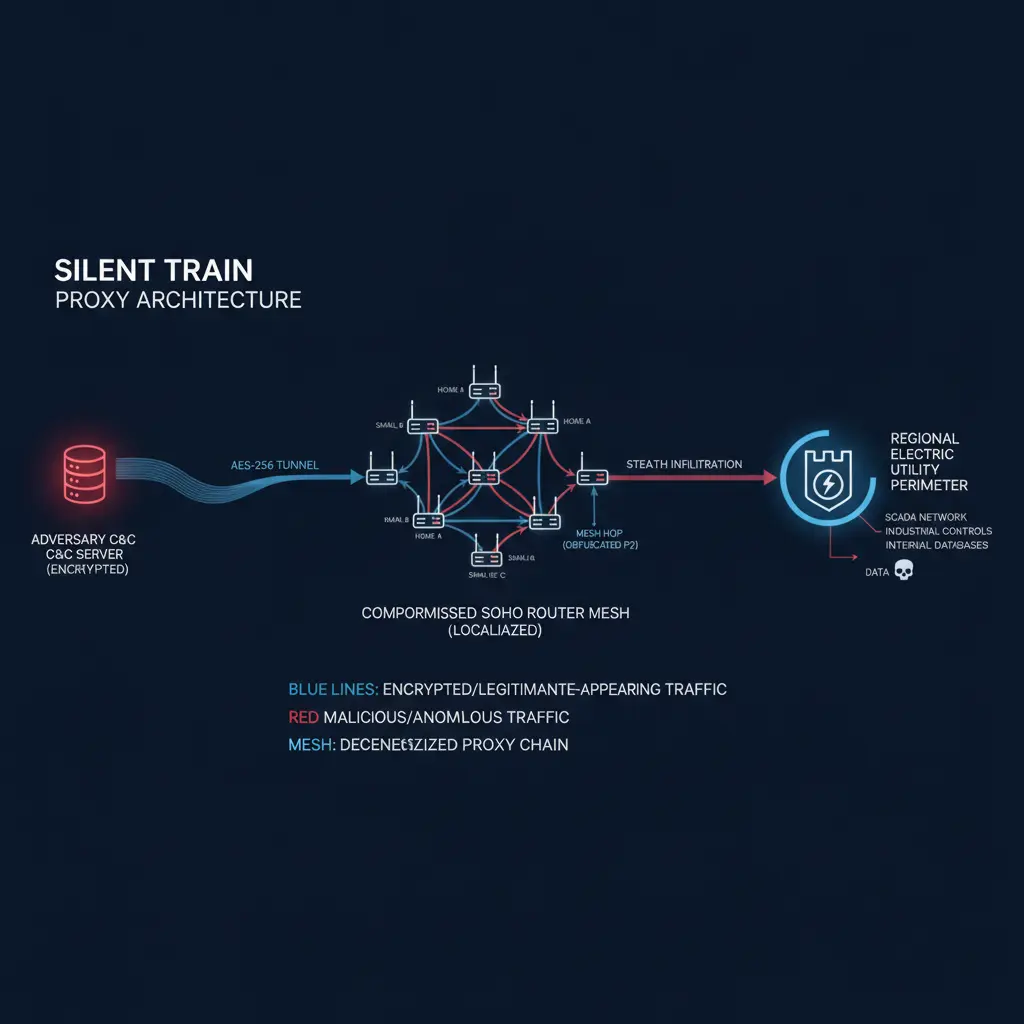
Attribution and tracking of VOLTZITE remain difficult due to their custom operational infrastructure known as "Silent Train." Departing from static command-and-control (C2) domains, the group orchestrates ephemeral multi-hop proxy chains across hijacked small office and home office (SOHO) devices. By exploiting unpatched TP-Link, Netgear Orbi, and legacy Cisco gateways, the actors assemble four-to-six-hop circuits that route administrative commands through the victim utility's immediate geographic municipality. To a regional security operations center, an interactive session originating from a local residential broadband address blends seamlessly with benign remote engineering traffic.
By leveraging MITRE ATT&CK T1090.002 (Proxy: External Proxy) (opens in a new tab), VOLTZITE conducts deep surveillance while frustrating external telemetry. Operators do not drop compiled binary implants on compromised systems. Instead, they interactively establish secure port forwards using native platform commands or minimalist tools like FRP and Chisel, effectively masquerading inside lawful transport tunnels.
Anatomical Reconnaissance: From Versa Director to SCADA Core
The pivot from perimeter compromise to SCADA network awareness follows a methodical, low-velocity progression. VOLTZITE targets the enterprise perimeter through MITRE ATT&CK T1190 (Exploit Public-Facing Application) (opens in a new tab). Once initial access is secured on devices such as Versa Director, the actors pivot horizontally toward Active Directory infrastructure, harvesting elevated credentials without executing custom malicious binaries.
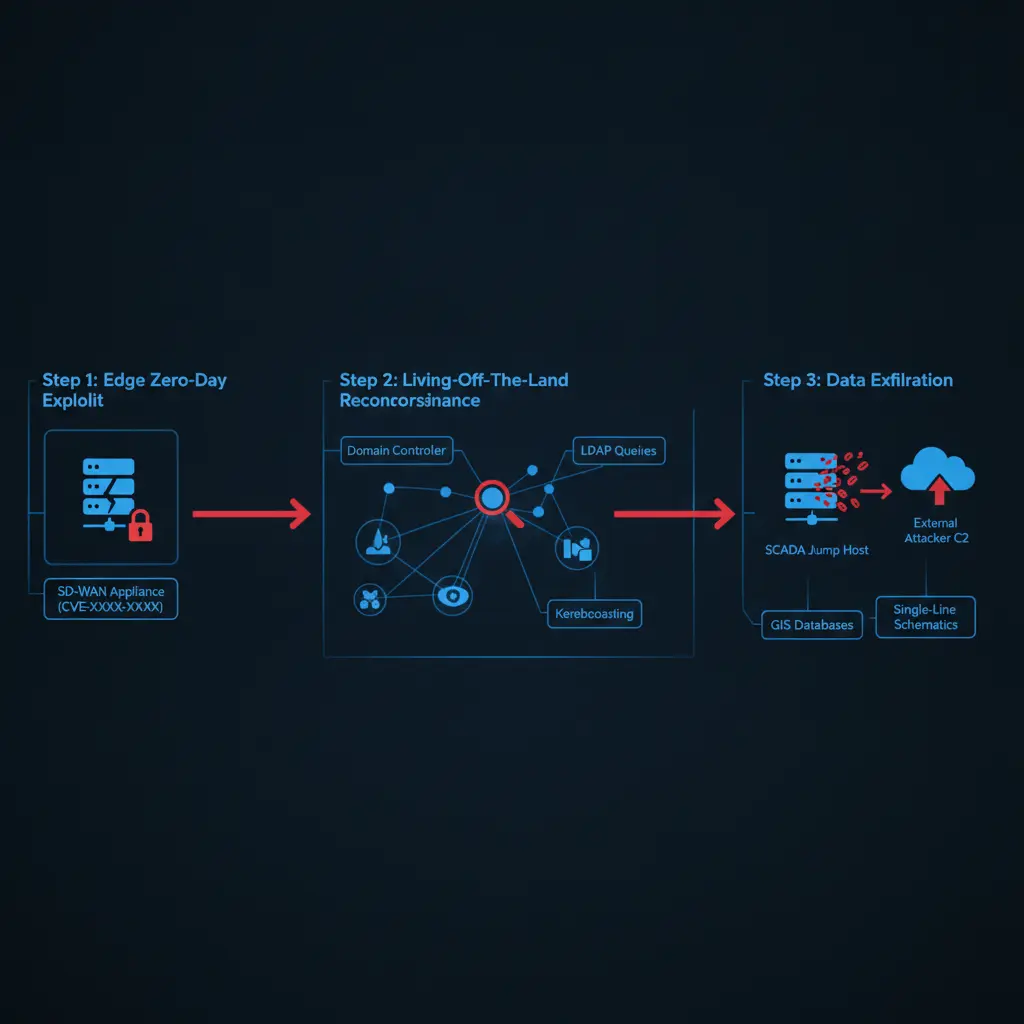
Upon establishing lateral access into network enclaves adjacent to the Industrial Demilitarized Zone (IDMZ), VOLTZITE avoids touching programmable logic controllers (PLCs) directly. Instead, operators focus on data harvesting that yields complete operational context:
GIS Topology Extraction: Exfiltrating spatial distribution maps to correlate physical substations with primary high-voltage transmission lines.
Single-Line Schematics: Documenting bus ties, breaker configurations, and transformer redundancy channels.
Engineering Station Artifacts: Stealing configuration files, Modbus register maps, DNP3 point lists, and IEC 60870-5-104 addressing schemes from Human-Machine Interface (HMI) workstations.
If you were the CISO reviewing the telemetry during these reconnaissance phases, you would not see custom malware detonations or anomalous port scans. You would see routine administrative utilities (nltest, wmic, netsh) executing during expected maintenance windows, punctuated by targeted, low-frequency directory queries for .vsd, .dwg, and .pdf schematic files.
Living-off-the-Land and Active Anti-Forensics
The hallmark of VOLTZITE's tradecraft is the total avoidance of signature-generating payloads. In accordance with MITRE ATT&CK T1059.001 (Command and Scripting Interpreter: PowerShell) (opens in a new tab), the group restricts post-exploitation activities to native command-line interfaces. System staging is orchestrated using built-in system tools: wmic for process and network discovery, netsh for port forwarding and interface mapping, and certutil for decoding base64-encoded administrative scripts.
**Representative living-off-the-land port proxy routine observed in actor tradecraft**
netsh interface portproxy add v4tov4 listenport=8443 listenaddress=0.0.0.0 connectport=443 connectaddress=192.168.10.15
Once an operational milestone is attained, anti-forensics protocols are triggered. Actors systematically invoke wevtutil cl to wipe security, system, and operational logs, purge temporary staging directories, and dismount shadow volumes. By clearing local event logs before terminating sessions, VOLTZITE deliberately breaks incident response timelines, converting what should be hours of digital triage into months of forensic reconstruction.
Proof of Concept: Auditing Exposed Management Interfaces and Proxy Artifacts
To identify vulnerable perimeter infrastructure and living-off-the-land persistence mechanisms leveraged by VOLTZITE, defensive teams must audit external endpoints and internal routing rules.
External Gateway Version Enumeration: Verify unauthenticated exposure of management interfaces across SD-WAN controllers to detect unpatched installations vulnerable to CVE-2024-39717.
bash curl -k -s -I "https://edge-gw.utility.internal:9182/versa/login" | grep -i "Versa-Director"Defenders should verify that administrative ports are strictly non-routable over public internet interfaces.
Audit Host-Level Port Forwarding: Identify unauthorized reverse proxies or forwarding conduits created via Windows
netshutility.powershell Get-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\PortProxy\v4tov4\tcp" -ErrorAction SilentlyContinueAny entry linking external perimeter interfaces directly to internal engineering jumps indicates a high-severity policy violation or ongoing compromise.
Event Log Anomaly Detection: Hunt for mass security log clearing invocations commonly associated with post-operation hygiene.
powershell Get-WinEvent -FilterHashtable @{LogName='System'; Id=104} | Select-Object TimeCreated, MessageEvent ID 104 in the System log signals deliberate event log purges, requiring immediate isolation of the host.
Structural Mitigations for SCADA Enclaves
Securing electric utility infrastructure against nation-state pre-positioning requires decisive architectural restructuring rather than incremental endpoint tooling:
Eradicate Dual-Homed Systems: Strictly enforce isolated jump-box bastions between IT networks and Operational Technology control rooms. Zero network paths should route directly from corporate email domains to substation gateways.
Deprecate Internet-Facing SD-WAN Management: Remove administrative consoles of perimeter network controllers (Versa Director, Cisco Catalyst SD-WAN) from public exposure. Enforce out-of-band management channels with hardware-backed FIDO2 authentication tokens.
Command-Line Telemetry Analytics: Shift detection paradigms from static hash scanning to behavioural parent-process telemetry. Alert automatically on administrative tools (
netsh,wevtutil,nltest,certutil) executed by non-standard parent binaries or web services.Passive OT Network Inspection: Implement continuous, non-intrusive monitoring of SCADA communication buses to flag unusual DNP3 point queries, unexpected RTU configuration downloads, and unapproved modifications to industrial control logic.
FINAL VERDICT
The targeted campaign led by VOLTZITE demonstrates that modern geopolitical conflict begins years before physical hostilities commence, conducted within the unsegmented boundaries of critical infrastructure. The vulnerability does not lie merely in edge appliance zero-days, but in an enterprise architecture that permits edge management compromises to expose industrial control systems. Board directors and utility executives who fail to enforce strict IT/OT perimeter boundaries, eliminate public administrative interfaces, and actively hunt for living-off-the-land persistence are leaving national power grids vulnerable to catastrophic disruption. BreachModal provides the adversarial simulations, perimeter hardening, and tactical incident response required to protect sovereign critical assets before the switch is flipped.